Free vendor security questionnaire template
Two versions you can download and send to a vendor today. They are the same questionnaire Vetrail itself sends.
Use the short version (24 questions, about 15 minutes for the vendor) for most vendors, and the full version (54 questions across 12 areas) for the few that hold your customers' data or keep your product running. Both are free to use and adapt for your own company. Each question says what a good answer looks like, and the questions that matter most are marked as critical.
| Version | Questions | Areas | Time for the vendor | Use it for | Download |
|---|---|---|---|---|---|
| Short | 24 | 6 | About 15 minutes | Most vendors, and a first screen of any vendor | Short version (CSV) |
| Full | 54 | 12 | About 40 minutes | Your most important vendors, such as those that hold customer data | Full version (CSV) |
The files open in Excel, Google Sheets or Numbers. Each row has the question, what a good answer looks like, whether the control is critical, its weight, and columns for the answer and the evidence.
What it covers
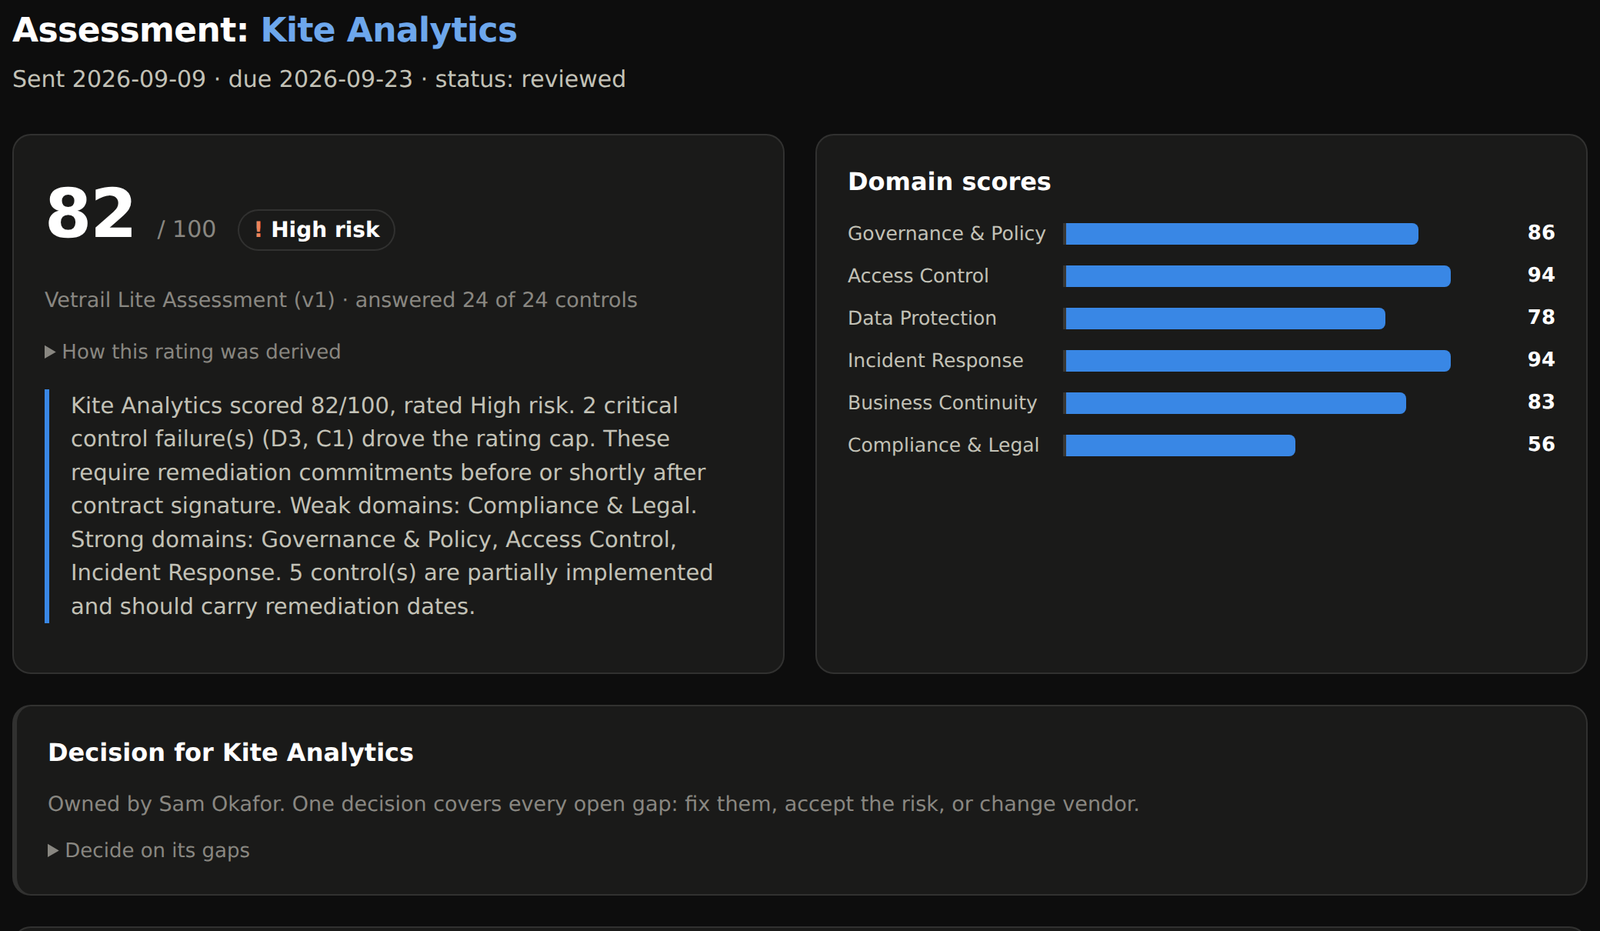
The short version asks about Governance & Policy, Access Control, Data Protection, Incident Response, Business Continuity, Compliance & Legal. The full version adds Secure Development & Change, Network & Cloud Security, Endpoint Security, Privacy, Third-Party Management, Physical Security.
These areas cover the same ground as the main security frameworks, such as the NIST Cybersecurity Framework. The template is not a mapping to any framework, and a vendor's answers do not show that it complies with one.
How to score it
- A Yes earns the question's full weight, a Partial earns half, and a No earns nothing. Not applicable is left out of the score, and the vendor should say why it does not apply.
- The score is the weight earned as a share of the weight possible, out of 100. A higher score means stronger controls.
- The score sets the risk rating: Low for 85 to 100, Medium for 70 to 84, High for 50 to 69, Critical for 0 to 49.
- A No on any critical control caps a Low or Medium rating at High, and three or more critical Nos make it Critical, whatever the score.
Sending it and getting it back
Give the vendor a due date, say why you are asking and who will see the answers, and ask for evidence behind the critical controls, such as a policy or an audit report. Then follow up on a fixed schedule rather than when you remember. Small customers often get no reply at all, which has its own guide: what to do when a vendor will not answer your questionnaire.
What a questionnaire cannot tell you
A questionnaire records what a vendor says. It does not check it. For a vendor that holds sensitive data, ask for independent evidence, such as a SOC 2 report or an ISO 27001 certificate, and read it. A questionnaire also says little about a vendor's finances or its own suppliers unless you ask. This template is not advice on what any regulator or auditor requires of you.
How Vetrail uses it
In Vetrail you choose the version for each vendor, and the vendor answers through a link without creating an account. Up to 5 reminders go out on a schedule, and the answers are scored by the rules above, so every vendor is rated the same way. It is free for up to 15 vendors and 5 people.
Start free or see how it works
Questions
Can I change the questions?
Yes. The file is yours to edit. If you change the weights or the critical marks, score every
vendor with the same version so the results stay comparable.
Is a completed questionnaire the same as a SOC 2 report?
No. A SOC 2 report is an auditor's opinion on a vendor's controls. A questionnaire is the
vendor's own account.
What if a vendor sends its own security pack instead?
Accept it if it answers the same questions, and note which questions it leaves out.
Sources
Vetrail is not affiliated with NIST. Last checked 9 November 2026.
Related
- Free vendor risk management software for small teams
- A free alternative to Vanta for vendor risk
- What to do when a vendor will not answer your questionnaire
- A risk register for a startup that keeps itself current
- Free ERM and ORM software for a startup or small business
- Risk register or ERM: what a small team needs
- Free startup risk register template
- A customer sent us a security questionnaire
- Key person risk: when one person holds the keys