What to do when a vendor will not answer your security questionnaire
Most advice on this assumes you are a bank the vendor cannot afford to ignore. This guide is for the other case: a small company asking a much larger vendor.
Assess what the vendor already publishes, ask for less, chase on a schedule, and write down your decision either way. A large vendor that ignores a small customer's questionnaire has often published enough about its security to assess it without one.
Five steps
- Start from what they publish. Many larger software vendors run a trust centre with their security documents, publish answers to a standard questionnaire, or share a SOC 2 report under a non-disclosure agreement. Read that before you send anything, and send questions only about what it leaves open.
- Ask for less. A long questionnaire sent to a vendor you pay a small subscription to will wait in a queue. A short screen of the controls that matter for what the vendor actually touches is an easier request to say yes to.
- Ask the right person. Your account manager or sales contact has a reason to reply. A general support inbox does not.
- Chase on a schedule, not from memory. Decide the reminder dates when you send the request, and decide what happens after the last one. Otherwise the request quietly expires and nobody notices.
- Decide, and record it. If the vendor stays silent you still have to make a call: keep using them with conditions, accept the gap until a set review date, or replace them. Record what you asked, what you found instead, who decided and when. A request with no answer and no decision is the gap a customer or auditor will find.
Banks and other regulated firms have more levers, such as escalating senior to senior or making the questionnaire a condition of the contract. Guidance written for them, such as Venminder's and Ncontracts', covers those. This page is general practice, not advice on what any regulator or auditor requires of you.
How Vetrail handles a silent vendor
- 100+ common vendors arrive pre-researched from their own public disclosures, so for many large vendors you may not need to ask at all.
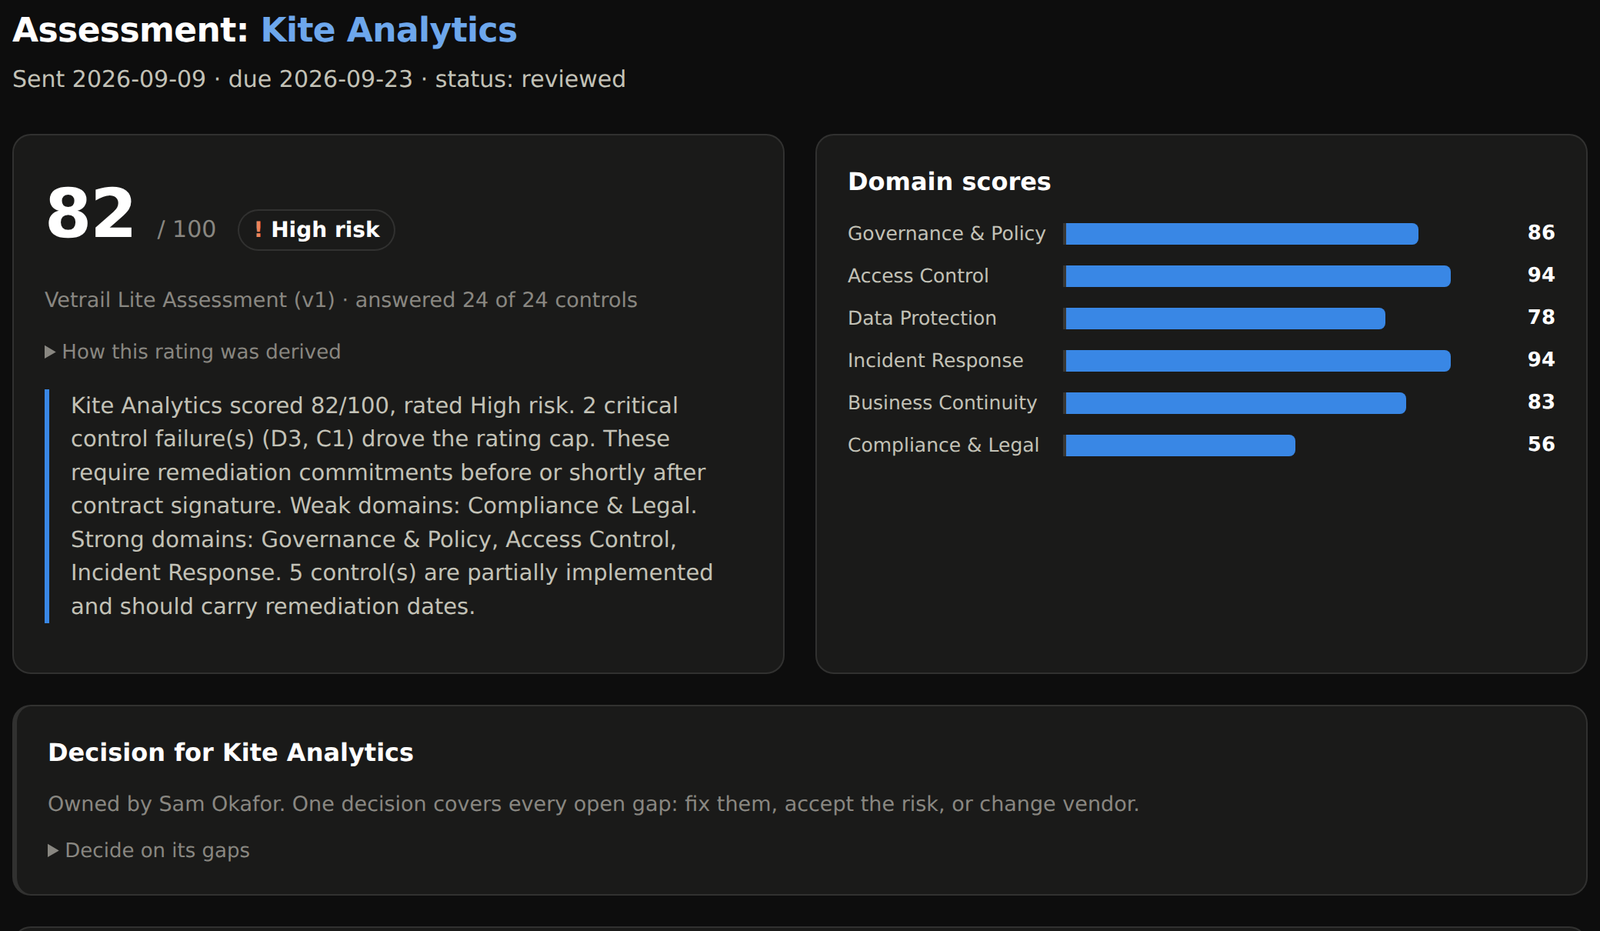
- Two sizes of questionnaire: a 24-control screen and a 54-control assessment, sent by link with no account for the vendor to create.
- A reminder ladder: by default a reminder goes out 7 and 3 days before the due date, on the due date, and 7 and 14 days after it, then one digest goes to a person on your team. Each workspace can set its own dates.
- Answer it yourself: when a vendor has no contact who will reply, a reviewer on your team can complete the assessment from the vendor's published evidence. It is recorded as answered by your team, not by the vendor.
Start free or explore the demo
Questions
The vendor only offers a SOC 2 report. Is that enough?
It often answers most of what a questionnaire would ask. Check that it covers the service you
use and a recent period, and read the exceptions the auditor noted. Then ask only about what it
leaves out.
How many reminders before I stop?
Vetrail's default is 5 reminders over 21 days, then
the decision goes to a person. What matters more than the number is that the dates are set in
advance and the last step is a decision, not silence.
Should I stop using a vendor who will not answer?
That depends on what the vendor touches and what you found without them. The point is to make
that call on purpose and write it down, rather than let the request lapse.
Sources
- What do I do if my vendor won't fill out the vendor risk assessment questionnaire?, Venminder
- How to get due diligence documents from a vendor, Ncontracts
- How Vetrail works
Last checked 21 October 2026.
Related
- Free vendor risk management software for small teams
- A free alternative to Vanta for vendor risk
- A risk register for a startup that keeps itself current
- Free ERM and ORM software for a startup or small business
- Risk register or ERM: what a small team needs
- Free vendor security questionnaire template
- Free startup risk register template
- A customer sent us a security questionnaire
- Key person risk: when one person holds the keys